Anti-VPN
阻止来自您 Minecraft 服务器的 VPN、代理和数据中心连接。
平台支持
要求
- Java: 11+(根据此插件说明;您的 Minecraft 服务器可能需要更高版本的 Java)。
- LuckPerms (可选 — 若无安装则回退至 Bukkit 权限系统)
- 首次启动时需联网以下载拦截列表 (此后即可离线运行)
功能特性
- 无需密钥检测 — 完全基于免费且开源的 IP 拦截列表
- SQLite 与 MySQL 支持 — 内置本地数据库或连接至您自己的外部服务器
- 四种组合拦截列表 — 涵盖攻击源、匿名器、商业 VPN 及数据中心
- 自动更新列表 — 在启动时按可配置的时间间隔从 GitHub 下载最新数据
- 本地列表缓存 — 所有列表均保存至磁盘并带有日期标记的备份,首次下载后即可离线工作
- 零登录延迟 — CIDR 匹配完全在内存中运行,每次连接仅需微秒级响应
- LuckPerms 集成 — 完整支持权限节点,可按组或玩家设置绕过权限
- 完全自定义消息 — 所有面向玩家的消息字符串均位于
messages.yml 中
- 游戏内管理 — 添加、移除和检查 IP 及玩家,无需触碰任何文件
图片展示
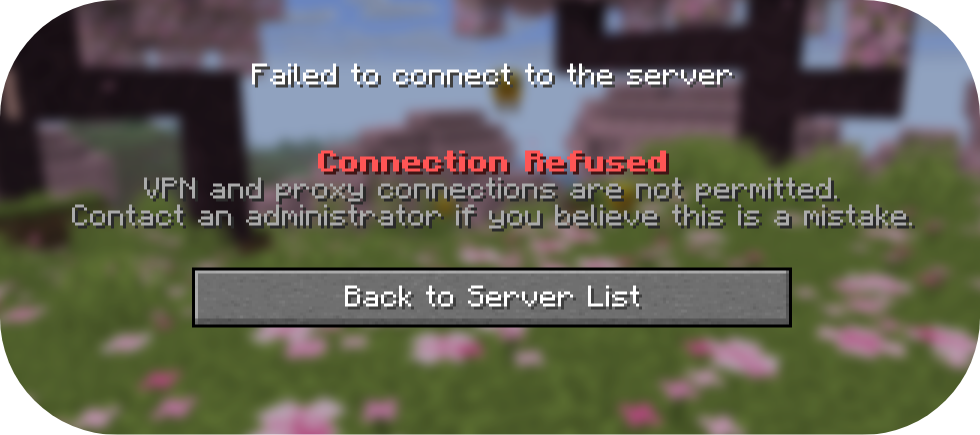
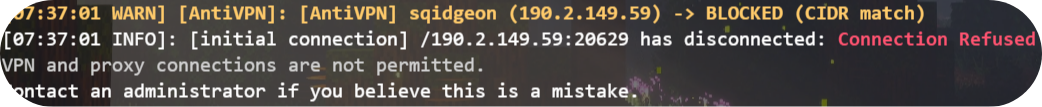
使用 VPN 时
未使用 VPN 时

检测原理
AntiVPN 将四个免费拦截列表合并为一个内存中的 CIDR 匹配器,能在毫秒级时间内检查每个连接的 IP:
| 列表 |
来源 |
覆盖范围 |
firehol_level1.netset |
Firehol |
攻击源、恶意软件、无效网段 |
firehol_anonymous.netset |
Firehol |
Tor、开放代理、匿名器 |
x4bnet_vpn.netset |
X4BNet |
ProtonVPN、Mullvad、NordVPN、ExpressVPN 等更多 |
x4bnet_datacenter.netset |
X4BNet |
AWS、OVH、Hetzner、DigitalOcean 等更多 |
所有列表将在首次启动时下载至 plugins/AntiVPN/firehol/ 目录并自动刷新。每次成功下载新数据时,都会保留带有日期标记的备份副本。
可选的反向 DNS 启发式检查会进一步将 PTR 记录与已知的 VPN/主机名模式进行比对,作为第二层防护。
数据库
AntiVPN 将封禁 IP、放行 IP 及绕过玩家存储于真实数据库中。
SQLite(默认 — 零配置):
database:
  type: sqlite
首次启动时自动创建 plugins/AntiVPN/antivpn.db。
MySQL / MariaDB(外部服务器):
database:
  type: mysql
  mysql:
    host: your.db.host
    port: 3306
    database: antivpn
    username: antivpn_user
    password: "yourpassword"
LuckPerms 权限
AntiVPN 开箱即用地集成了 LuckPerms。如果未安装 LuckPerms,它会自动回退到 Bukkit 权限系统。
| 权限 |
默认值 |
描述 |
antivpn.admin |
OP |
所有权限,包括绕过权限 |
antivpn.bypass |
false |
在登录时跳过所有 VPN 检查 |
antivpn.allow |
OP |
使用 /ipallow |
antivpn.block |
OP |
使用 /ipblock |
antivpn.list |
OP |
使用 /iplist |
antivpn.user |
OP |
使用 /ipuser |
antivpn.update |
OP |
使用 /ipupdate |
通过 LuckPerms 为某个组授予绕过权限:
/lp group vip permission set antivpn.bypass true
命令
/ipblock — 管理 IP 拦截列表
| 子命令 |
描述 |
/ipblock add <ip> |
封禁一个 IP 地址 |
/ipblock remove <ip> |
解除对一个 IP 地址的封禁 |
/ipblock list |
显示所有手动封禁的 IP |
/ipblock check <ip> |
显示某个 IP 的封禁/放行状态 |
/ipallow — 管理 IP 放行列表
| 子命令 |
描述 |
/ipallow add <ip> |
将 IP 加入白名单(跳过所有检查) |
/ipallow remove <ip> |
从放行列表中移除 |
/ipallow list |
显示所有放行的 IP |
/ipuser — 管理绕过玩家
| 子命令 |
描述 |
/ipuser add <player> |
使某玩家豁免所有 VPN 检查 |
/ipuser remove <player> |
移除豁免权 |
/ipuser list |
显示所有绕过玩家 |
/ipuser check <player> |
检查某玩家的绕过状态 |
/ipuser lookup <player> |
显示在线玩家的 IP 及完整状态 |
/iplist — 查看所有列表
| 子命令 |
描述 |
/iplist |
所有列表大小的摘要 |
/iplist blocked |
完整的封禁 IP 列表 |
/iplist allowed |
完整的放行 IP 列表 |
/iplist users |
完整的绕过玩家列表 |
/ipupdate — 管理拦截列表
| 子命令 |
描述 |
/ipupdate |
立即强制下载所有列表 |
/ipupdate status |
显示列表文件大小、日期及当前活跃的 CIDR 数量 |
/ipupdate reload |
从现有本地文件重新加载匹配器 |
/ipupdate backups |
列出所有带日期标记的备份文件 |
配置
config.yml
log-connections: true

database:
  type: sqlite         # 或 "mysql"

列表:
  firehol-level1: true
  firehol-anonymous: true
  x4bnet-vpn: true        # 覆盖 ProtonVPN、Mullvad、NordVPN 等
  x4bnet-datacenter: true # 覆盖 AWS、OVH、Hetzner 等

firehol:
  update-interval-hours: 24
  force-update-on-start: false

reverse-dns-check: true
messages.yml
插件发送的每条消息均可完全自定义。支持 & 颜色代码和 {占位符}。
general:
  prefix: "&8[&cAntiVPN&8] &r"

kick:
  message: "&c&l连接被拒绝\n&7不允许使用 VPN 连接。"

ipblock:
  added: "{prefix}&c{ip} &7已被添加到黑名单中。"
  # ... 以及更多选项
文件结构
首次启动后,你的插件文件夹将如下所示:
plugins/AntiVPN/
├── antivpn.db                          ← SQLite 数据库(包含所有列表)
├── config.yml
├── messages.yml
└── firehol/
    ├── firehol_level1.netset
    ├── firehol_anonymous.netset
    ├── x4bnet_vpn.netset
    ├── x4bnet_datacenter.netset
    └── *.bak                           ← 每个列表的带日期备份
支持
本项目由 sqidgeon 维护。未经我们同意,严禁重新分发此插件!
Anti-VPN
Block VPN, proxy, and datacenter connections from your Minecraft server.
Platforms
Requirements
- Java: 11+ according to this plugin description; your Minecraft server may require a newer Java version.
- LuckPerms (optional — falls back to Bukkit permissions)
- Internet access on first start to download blocklists (works offline after that)
Features
- Key-free detection — powered entirely by free, open-source IP blocklists
- SQLite & MySQL support — built-in local database or connect to your own external server
- Four combined blocklists — covering attacks, anonymizers, commercial VPNs, and datacenters
- Auto-updating lists — downloads fresh data from GitHub on startup and on a configurable schedule
- Local list caching — all lists saved to disk with dated backups, works offline after first download
- Zero login lag — CIDR matching runs entirely in-memory, microsecond-fast per connection
- LuckPerms integration — full permission node support with per-group and per-player bypass
- Fully customisable messages — every player-facing string lives in
messages.yml
- In-game management — add, remove, and inspect IPs and players without touching any files
Images
With a VPN
Without a VPN
How Detection Works
AntiVPN combines four free blocklists into a single in-memory CIDR matcher that checks every connecting IP in milliseconds:
| List |
Source |
Covers |
firehol_level1.netset |
Firehol |
Attacks, malware, bogon ranges |
firehol_anonymous.netset |
Firehol |
Tor, open proxies, anonymizers |
x4bnet_vpn.netset |
X4BNet |
ProtonVPN, Mullvad, NordVPN, ExpressVPN & more |
x4bnet_datacenter.netset |
X4BNet |
AWS, OVH, Hetzner, DigitalOcean & more |
All lists are downloaded to plugins/AntiVPN/firehol/ on first start and automatically refreshed. Dated backup copies are kept every time a new download succeeds.
An optional reverse-DNS heuristic further checks PTR records against known VPN/hosting hostname patterns as a secondary layer.
Database
AntiVPN stores blocked IPs, allowed IPs, and bypass players in a real database.
SQLite (default — zero setup):
database:
  type: sqlite
Creates plugins/AntiVPN/antivpn.db automatically on first start.
MySQL / MariaDB (external server):
database:
  type: mysql
  mysql:
    host: your.db.host
    port: 3306
    database: antivpn
    username: antivpn_user
    password: "yourpassword"
LuckPerms Permissions
AntiVPN integrates with LuckPerms out of the box. If LuckPerms isn't installed it falls back to Bukkit permissions automatically.
| Permission |
Default |
Description |
antivpn.admin |
OP |
All permissions including bypass |
antivpn.bypass |
false |
Skip all VPN checks at login |
antivpn.allow |
OP |
Use /ipallow |
antivpn.block |
OP |
Use /ipblock |
antivpn.list |
OP |
Use /iplist |
antivpn.user |
OP |
Use /ipuser |
antivpn.update |
OP |
Use /ipupdate |
Grant bypass to a group via LuckPerms:
/lp group vip permission set antivpn.bypass true
Commands
/ipblock — Manage the IP block-list
| Subcommand |
Description |
/ipblock add <ip> |
Block an IP address |
/ipblock remove <ip> |
Unblock an IP address |
/ipblock list |
Show all manually blocked IPs |
/ipblock check <ip> |
Show block/allow status of an IP |
/ipallow — Manage the IP allow-list
| Subcommand |
Description |
/ipallow add <ip> |
Whitelist an IP (bypasses all checks) |
/ipallow remove <ip> |
Remove from allow-list |
/ipallow list |
Show all allowed IPs |
/ipuser — Manage bypass players
| Subcommand |
Description |
/ipuser add <player> |
Exempt a player from all VPN checks |
/ipuser remove <player> |
Remove exemption |
/ipuser list |
Show all bypass players |
/ipuser check <player> |
Check a player's bypass status |
/ipuser lookup <player> |
Show an online player's IP and full status |
/iplist — View all lists
| Subcommand |
Description |
/iplist |
Summary of all list sizes |
/iplist blocked |
Full blocked IP list |
/iplist allowed |
Full allowed IP list |
/iplist users |
Full bypass player list |
/ipupdate — Manage blocklists
| Subcommand |
Description |
/ipupdate |
Force-download all lists now |
/ipupdate status |
Show list file sizes, dates, and active CIDR count |
/ipupdate reload |
Reload matcher from existing local files |
/ipupdate backups |
List all dated backup files |
Configuration
config.yml
log-connections: true

database:
  type: sqlite         # or "mysql"

lists:
  firehol-level1: true
  firehol-anonymous: true
  x4bnet-vpn: true        # Covers ProtonVPN, Mullvad, NordVPN etc.
  x4bnet-datacenter: true # Covers AWS, OVH, Hetzner etc.

firehol:
  update-interval-hours: 24
  force-update-on-start: false

reverse-dns-check: true
messages.yml
Every message the plugin sends is fully customisable. Supports & colour codes and {placeholders}.
general:
  prefix: "&8[&cAntiVPN&8] &r"

kick:
  message: "&c&lConnection Refused\n&7VPN connections are not permitted."

ipblock:
  added: "{prefix}&c{ip} &7has been added to the block-list."
  # ... and many more
File Structure
After first startup your plugin folder will look like this:
plugins/AntiVPN/
├── antivpn.db                          ← SQLite database (all your lists)
├── config.yml
├── messages.yml
└── firehol/
    ├── firehol_level1.netset
    ├── firehol_anonymous.netset
    ├── x4bnet_vpn.netset
    ├── x4bnet_datacenter.netset
    └── *.bak                           ← Dated backups of each list
Support
This project is maintained by sqidgeon. You are NOT allowed to re-distribute this plugin without consent from us!


 插件

 插件

 插件
 插件
 插件
 插件

评论 0
登录后参与评分
还没有评论,来抢沙发吧