Censera's Eye
Censera's Eye 是一款适用于离线模式服务器的 Paper 插件,它将身份验证与玩家信任机制分离。
未获得服务器信任的玩家加入时将进入访客模式(Visitor Mode)。他们可以注册并登录,但仅登录并不能获得正常权限。只有经过身份验证且被列入白名单后,玩家才能获得完整访问权限。
访客模式
访客模式旨在为那些将“加入服务器”和“获得服务器信任”视为两个独立概念的服务器提供支持。
访客无法执行以下操作:
- 使用普通命令
- 与方块或物品栏交互
- 攻击玩家或其他实体
- 拾取或丢弃物品
- 离开其访客活动区域
- 进入下界或末地
- 使用会将其带出允许区域的传送功能
访客活动区域基于玩家进入访客模式时的位置确定。每位玩家拥有独立的边界范围。
已成功注册但未列入白名单的玩家仍保持访客状态;已列入白名单但尚未完成身份验证的玩家也保持访客状态。
身份验证
Censera's Eye 为离线模式服务器提供账户注册与登录功能。
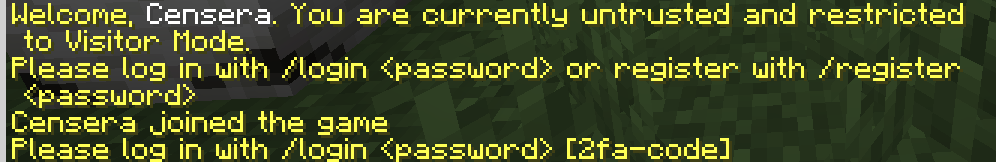
/register <password>
/login <password> [2fa-code]

/2fa enable
/2fa confirm <code>
/2fa disable <code>
密码采用加盐 PBKDF2 配合 HMAC SHA256 进行存储。TOTP 可作为第二重身份验证因素启用。
FastLogin 可用于正版玩家的认证。Floodgate 可配合 Geyser 用于基岩版玩家的接入。


为何采用此方案?
大多数身份验证插件侧重于防止他人冒用玩家名称。
Censera's Eye 还控制未信任玩家在加入服务器后可执行的操作。
这使得该插件特别适合希望实现以下目标的服务器:
- 在离线模式下运行,但不给予新玩家正常访问权限
- 将白名单作为真实的信任决策依据
- 允许新玩家连接,同时不让他们暴露于世界环境中
- 通过同一系统支持 Java 版和基岩版玩家
管理命令
/eyec reload
/eyec list
/eyec kick-visitors
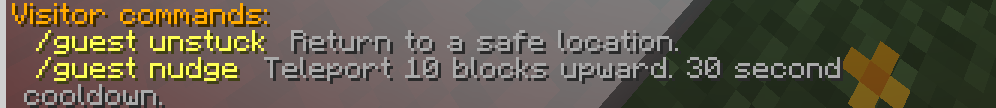
访客命令:
/guest unstuck
/guest nudge
管理员权限节点:
eyec.admin
eyec.bypass
集成支持
Censera's Eye 无需对这些插件进行数据包钩子集成。
工作原理
新玩家遵循以下流程:
加入 -> 访客模式 -> 身份验证 -> 白名单 -> 完整访问权限
身份验证用于确认账户归属。
白名单用于判断玩家是否可信。
Censera's Eye 将这两项决策分开处理,并在两者之间强制执行相应的限制。
如有任何问题或建议,请使用 GitHub Issues。
Censera's Eye
Eye is a Paper plugin for offline mode servers that keeps authentication separate from player trust.
Players who join without being trusted by the server are placed in Visitor Mode. They can register and log in, but logging in alone does not give them normal access. A player gets full access only after they have authenticated and are on the server whitelist.
Visitor Mode
Visitor Mode is intended for servers where joining the server and being trusted by the server are separate things.
Visitors cannot:
- use normal commands
- interact with blocks or inventories
- attack players or entities
- pick up or drop items
- leave their visitor area
- enter the Nether or End
- use teleports that would take them outside the allowed area
The visitor area is based on the location where the player entered Visitor Mode. Each player has their own boundary.
A player who has registered successfully but is not on the whitelist remains a visitor. A player who is on the whitelist but has not authenticated also remains a visitor.
Authentication
Censera's Eye provides account registration and login for offline mode servers.
/register <password>
/login <password> [2fa-code]

/2fa enable
/2fa confirm <code>
/2fa disable <code>
Passwords are stored using salted PBKDF2 with HMAC SHA256. TOTP can be enabled as a second authentication factor.
FastLogin can be used for premium player authentication. Floodgate can be used for Bedrock players through Geyser.
Why this approach?
Most authentication plugins focus on making sure that nobody else can use a player's name.
Censera's Eye also controls what an untrusted player can do after joining the server.
This makes it useful for servers that want to:
- run in offline mode without giving new players normal access
- use the whitelist as a real trust decision
- allow new players to connect without exposing the world to them
- support Java and Bedrock players through the same system
Administration
/eyec reload
/eyec list
/eyec kick-visitors
Visitor commands:
/guest unstuck
/guest nudge
Administrative permissions:
eyec.admin
eyec.bypass
Integrations
Censera's Eye does not require packet hooks into these plugins.
How it works
A new player follows this path:
Join -> Visitor Mode -> Authenticate -> Whitelist -> Full access
Authentication confirms the account.
The whitelist determines whether the player is trusted.
Eye keeps those two decisions separate and enforces the restrictions between them.
For any issues or recommendations, use GitHub Issues.


 插件

 插件
 插件
 插件
 插件
 插件
评论 0
登录后参与评分
还没有评论,来抢沙发吧